By Wadulo Arnold Mark
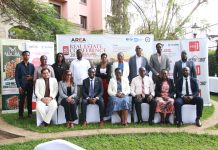
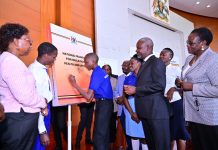
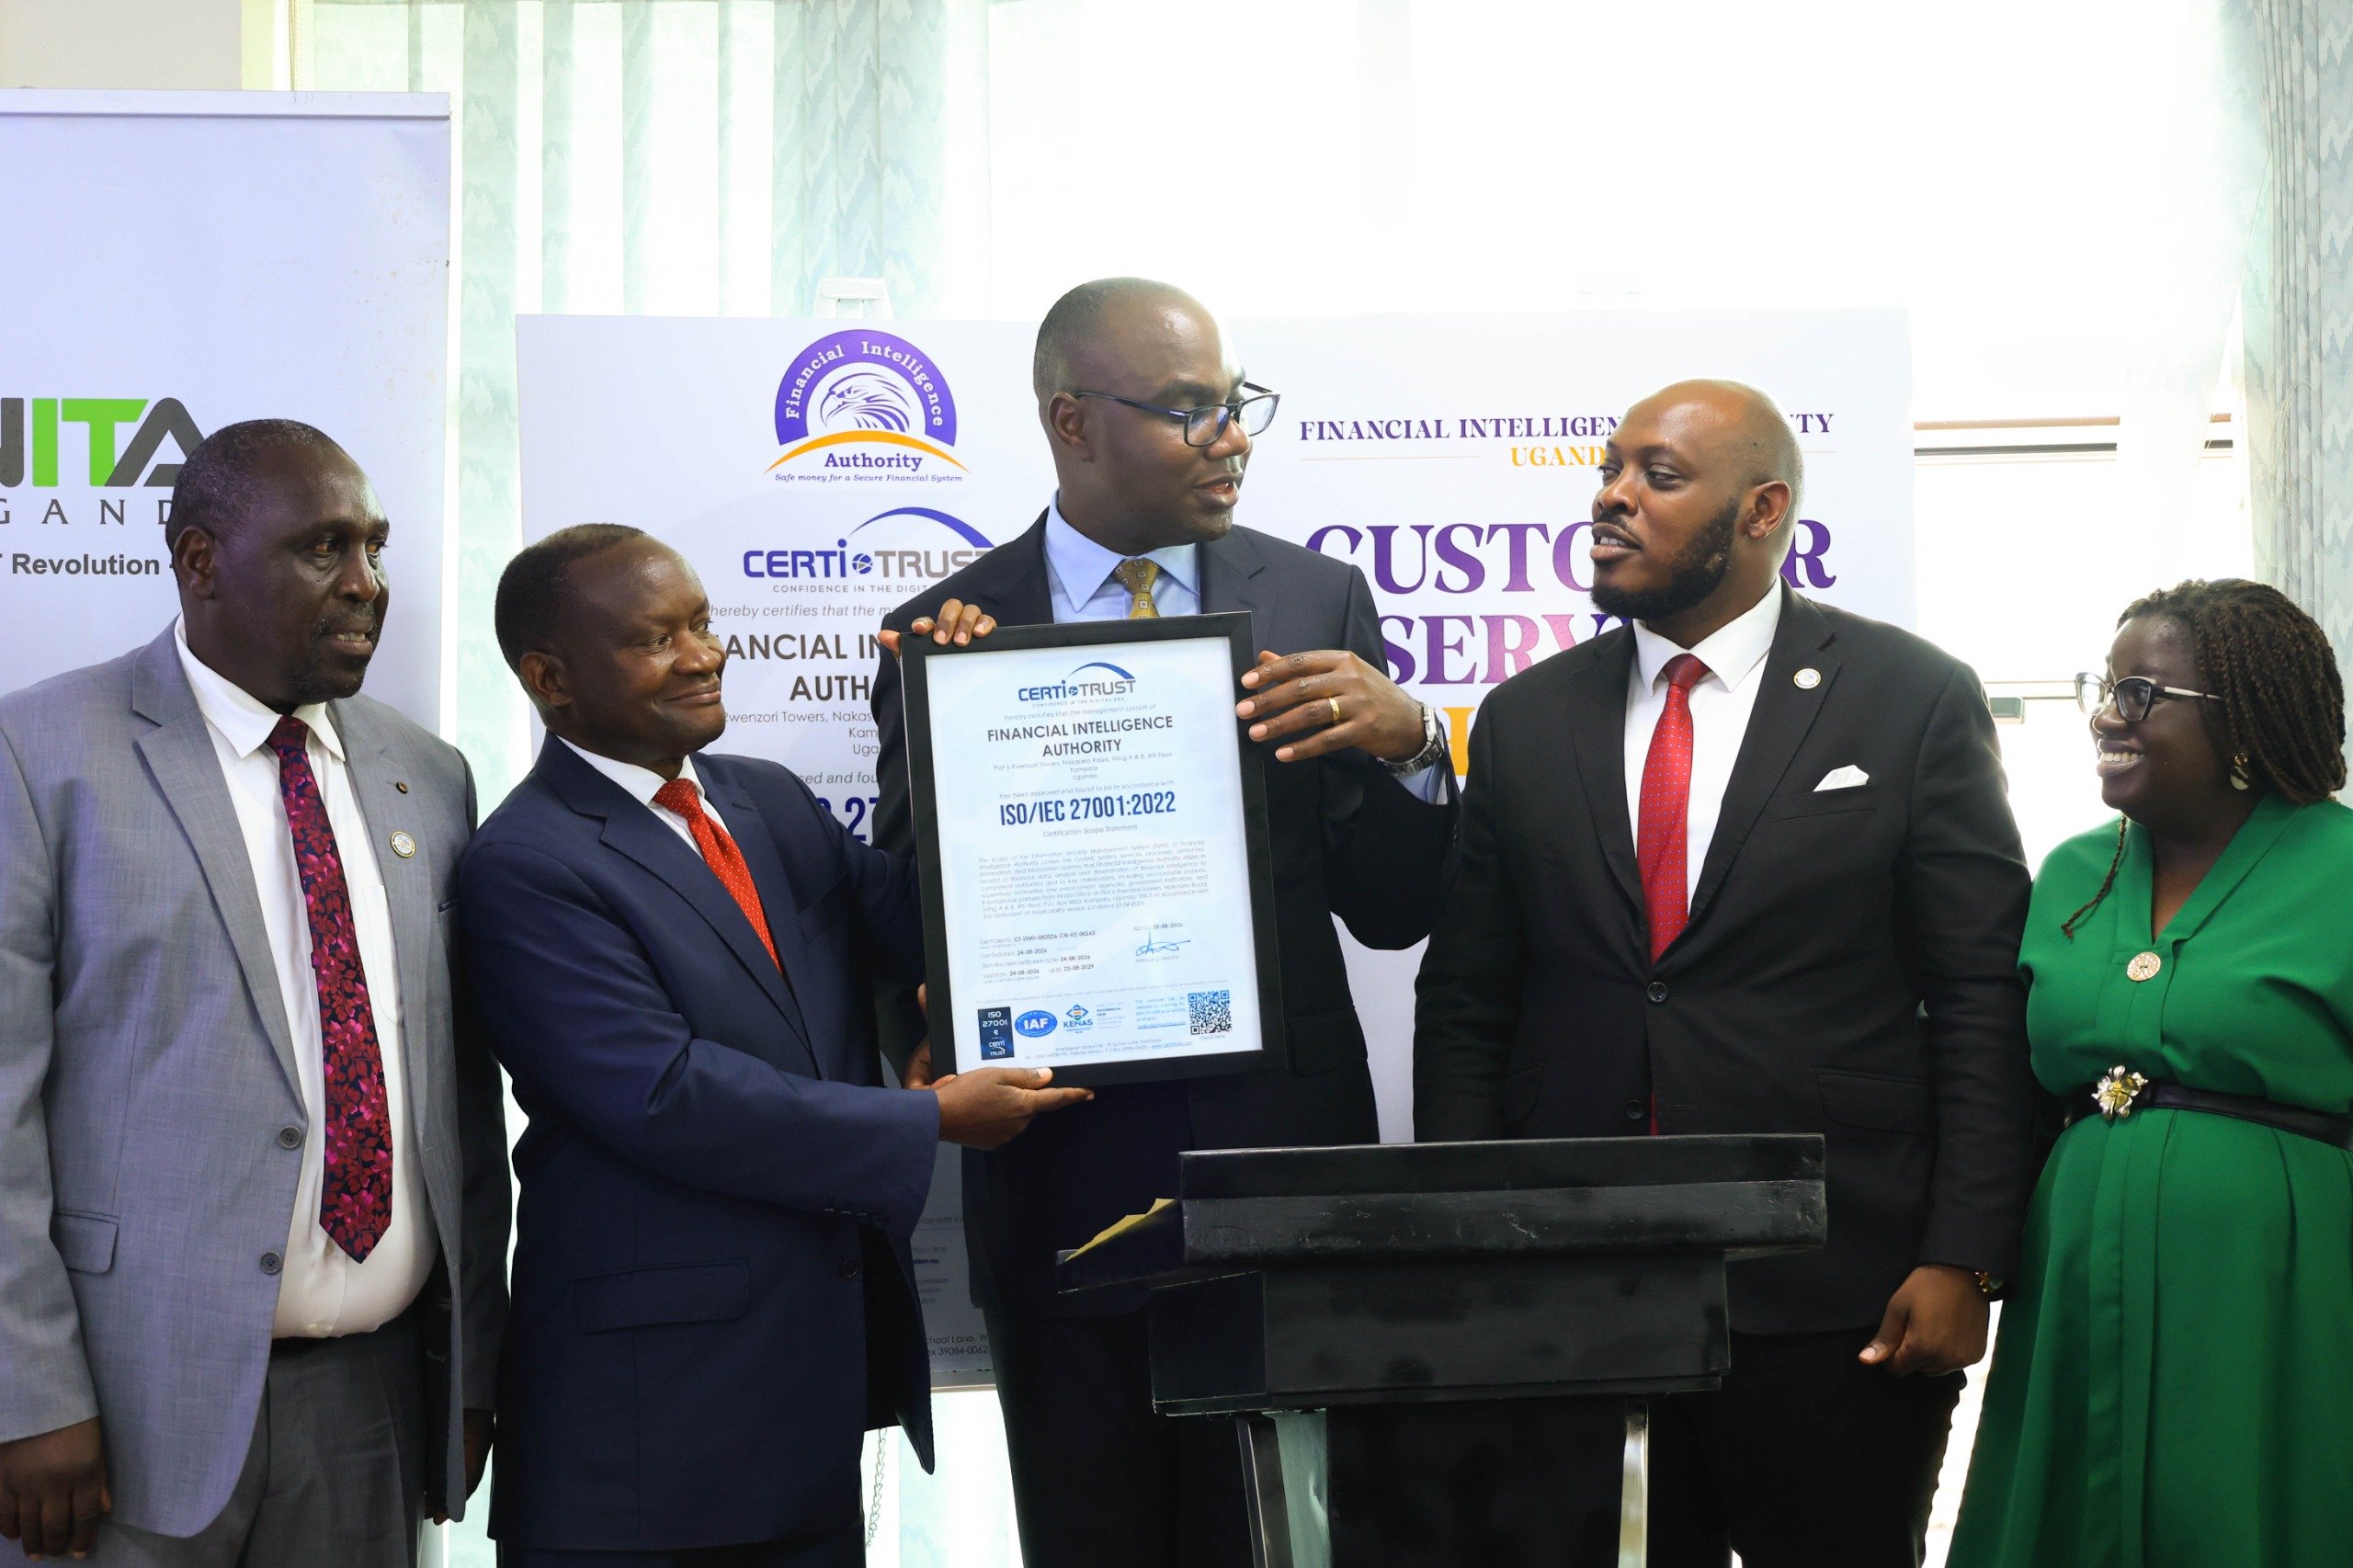
When the Financial Intelligence Authority (FIA) and its guests gathered at their Rwenzori Courts Kampala Head office to celebrate becoming the first Financial Intelligence Unit (FIU) among 51 in Africa to earn the ISO/IEC 27001:2022 cybersecurity certification, the atmosphere was equal parts high-stakes financial diplomacy and stand-up comedy. Presiding over the dual milestone which included launching the FIA Client Service Charter Minister for Finance Henry Musasizi delivered a speech in lighthearted banter backed by serious institutional warnings.
Musasizi wasted no time setting the record straight on government hierarchy and budget controls. After an earlier speaker commended the FIA Board for funding the security upgrade, Musasizi playfully interjected to correct the room on who actually controls the purse strings. “When we send you boards, the boards come here and become everything,” Musasizi joked, referring to Board Chairman Alinaffe Kalule. “The chairman is here on my behalf. Therefore, when I’m here, you should not thank him; you should only appreciate him when I’m not here, because he doesn’t have money to give you I am the one who carries the purse!”.
Yet beneath the Ministerial wit lay sharp critical scrutiny regarding Uganda’s standing in global finance. Supported by World Bank funding under the USD 160 million Digital Acceleration Project via NITA-Uganda, the ISO certification confirms that FIA’s information security systems meet rigorous international benchmarks for data confidentiality. Without airtight cybersecurity, leaking such sensitive financial intelligence would devastate investor trust and jeopardize national security.
However, as Musasizi candidly observed, ISO accreditation is an operational baseline, not a victory lap. With Uganda preparing for its 2028 Eastern and Southern Africa Anti-Money Laundering Group (ESAAMLG) mutual evaluation and actively drafting legislation to regulate virtual assets like USDT and cryptocurrencies the Minister delivered a humorous yet unmistakable ultimatum to FIA Executive Director Samuel Wandera.
“I hope Wandera you still want your job!” Musasizi laughed, warning that if the 2028 evaluation yields poor results, senior management would have no reason to stay. Urging the agency to pivot from African leadership to global competition, Musasizi reaffirmed the Ministry’s commitment to resourcing the fight against money laundering.
In an exclusive media interview following the ceremony, FIA Executive Director Samuel Were Wandera detailed the technical imperative of subjecting the agency’s data infrastructure to international audits. Wandera emphasized that strict cybersecurity safeguards are essential to maintain trust with commercial banks and intelligence partners.
“We are trusted with very vital information from accountable persons, mainly private financial data,” Wandera explained. “Under Ugandan law, reporting entities like commercial banks are required to inform us of cash transactions of 20 million shillings and above. Such confidential intelligence must remain strictly between the bank and the FIA until formal investigation and prosecution begin. This international accreditation demonstrates that we have put in place strong mechanisms so unauthorized persons and hackers cannot access the data we keep”.
Wandera further outlined how the certification positions Uganda to manage emerging financial technologies, including virtual assets and cryptocurrencies.
“Acquisition of this certificate confirms that our IT environment has gone through a vigorous assessment by international reviewers and meets global standards for a secure operating environment,” Wandera noted. “As technological developments evolve including virtual assets like USDT and digital currencies we are aligning our regulatory frameworks and building technical capacity to give total assurance to our local and international partners that all shared intelligence is handled with maximum security”.
Detailing the project’s scope and MDA selection criteria, NITA-Uganda Acting Director of Information Security Services Johnson Tumusiime explained that the initiative targeted ten key government institutions across strategic sectors. These include the Electricity Regulatory Authority, Petroleum Authority of Uganda, Public Procurement and Disposal of Public Assets Authority (PPDA), Insurance Regulatory Authority, National Drug Authority, Personal Data Protection Office, and the Deposit Protection Fund.
“The project selected 10 entities based on sectors and compliance assessments under the national information security framework to evaluate maturity and readiness,” Tumusiime stated. “FIA was prioritized because of its high institutional maturity, organized structure, and competent technical team. Out of the 10 targeted government entities, FIA and PPDA are the first to be fully certified” he concluded.